What is Art. 9 data?
Health data is one of the special categories of personal data under Art. 9 GDPR. Its processing is subject to the strictest rules the GDPR has.
 Larger organisation? Onboarding, training and a dedicated contact person.
Process patient data securely and in compliance with the law: what Art. 9 GDPR requires and how Logicc protects health data.
Health data is one of the special categories of personal data under Art. 9 GDPR. Its processing is subject to the strictest rules the GDPR has.
DPA, storage in Germany, Zero Data Retention with all model providers as far as technically possible, and for doctors and healthcare professionals the agreement under § 203 StGB from the Secure+ plan.
You carry out the data protection impact assessment yourself as the controller. And you decide how long chats are stored, from 30 days to unlimited.
You can delete individual documents and entire chat histories yourself at any time, irreversibly. When the contract ends, all data is deleted unless statutory retention obligations apply.
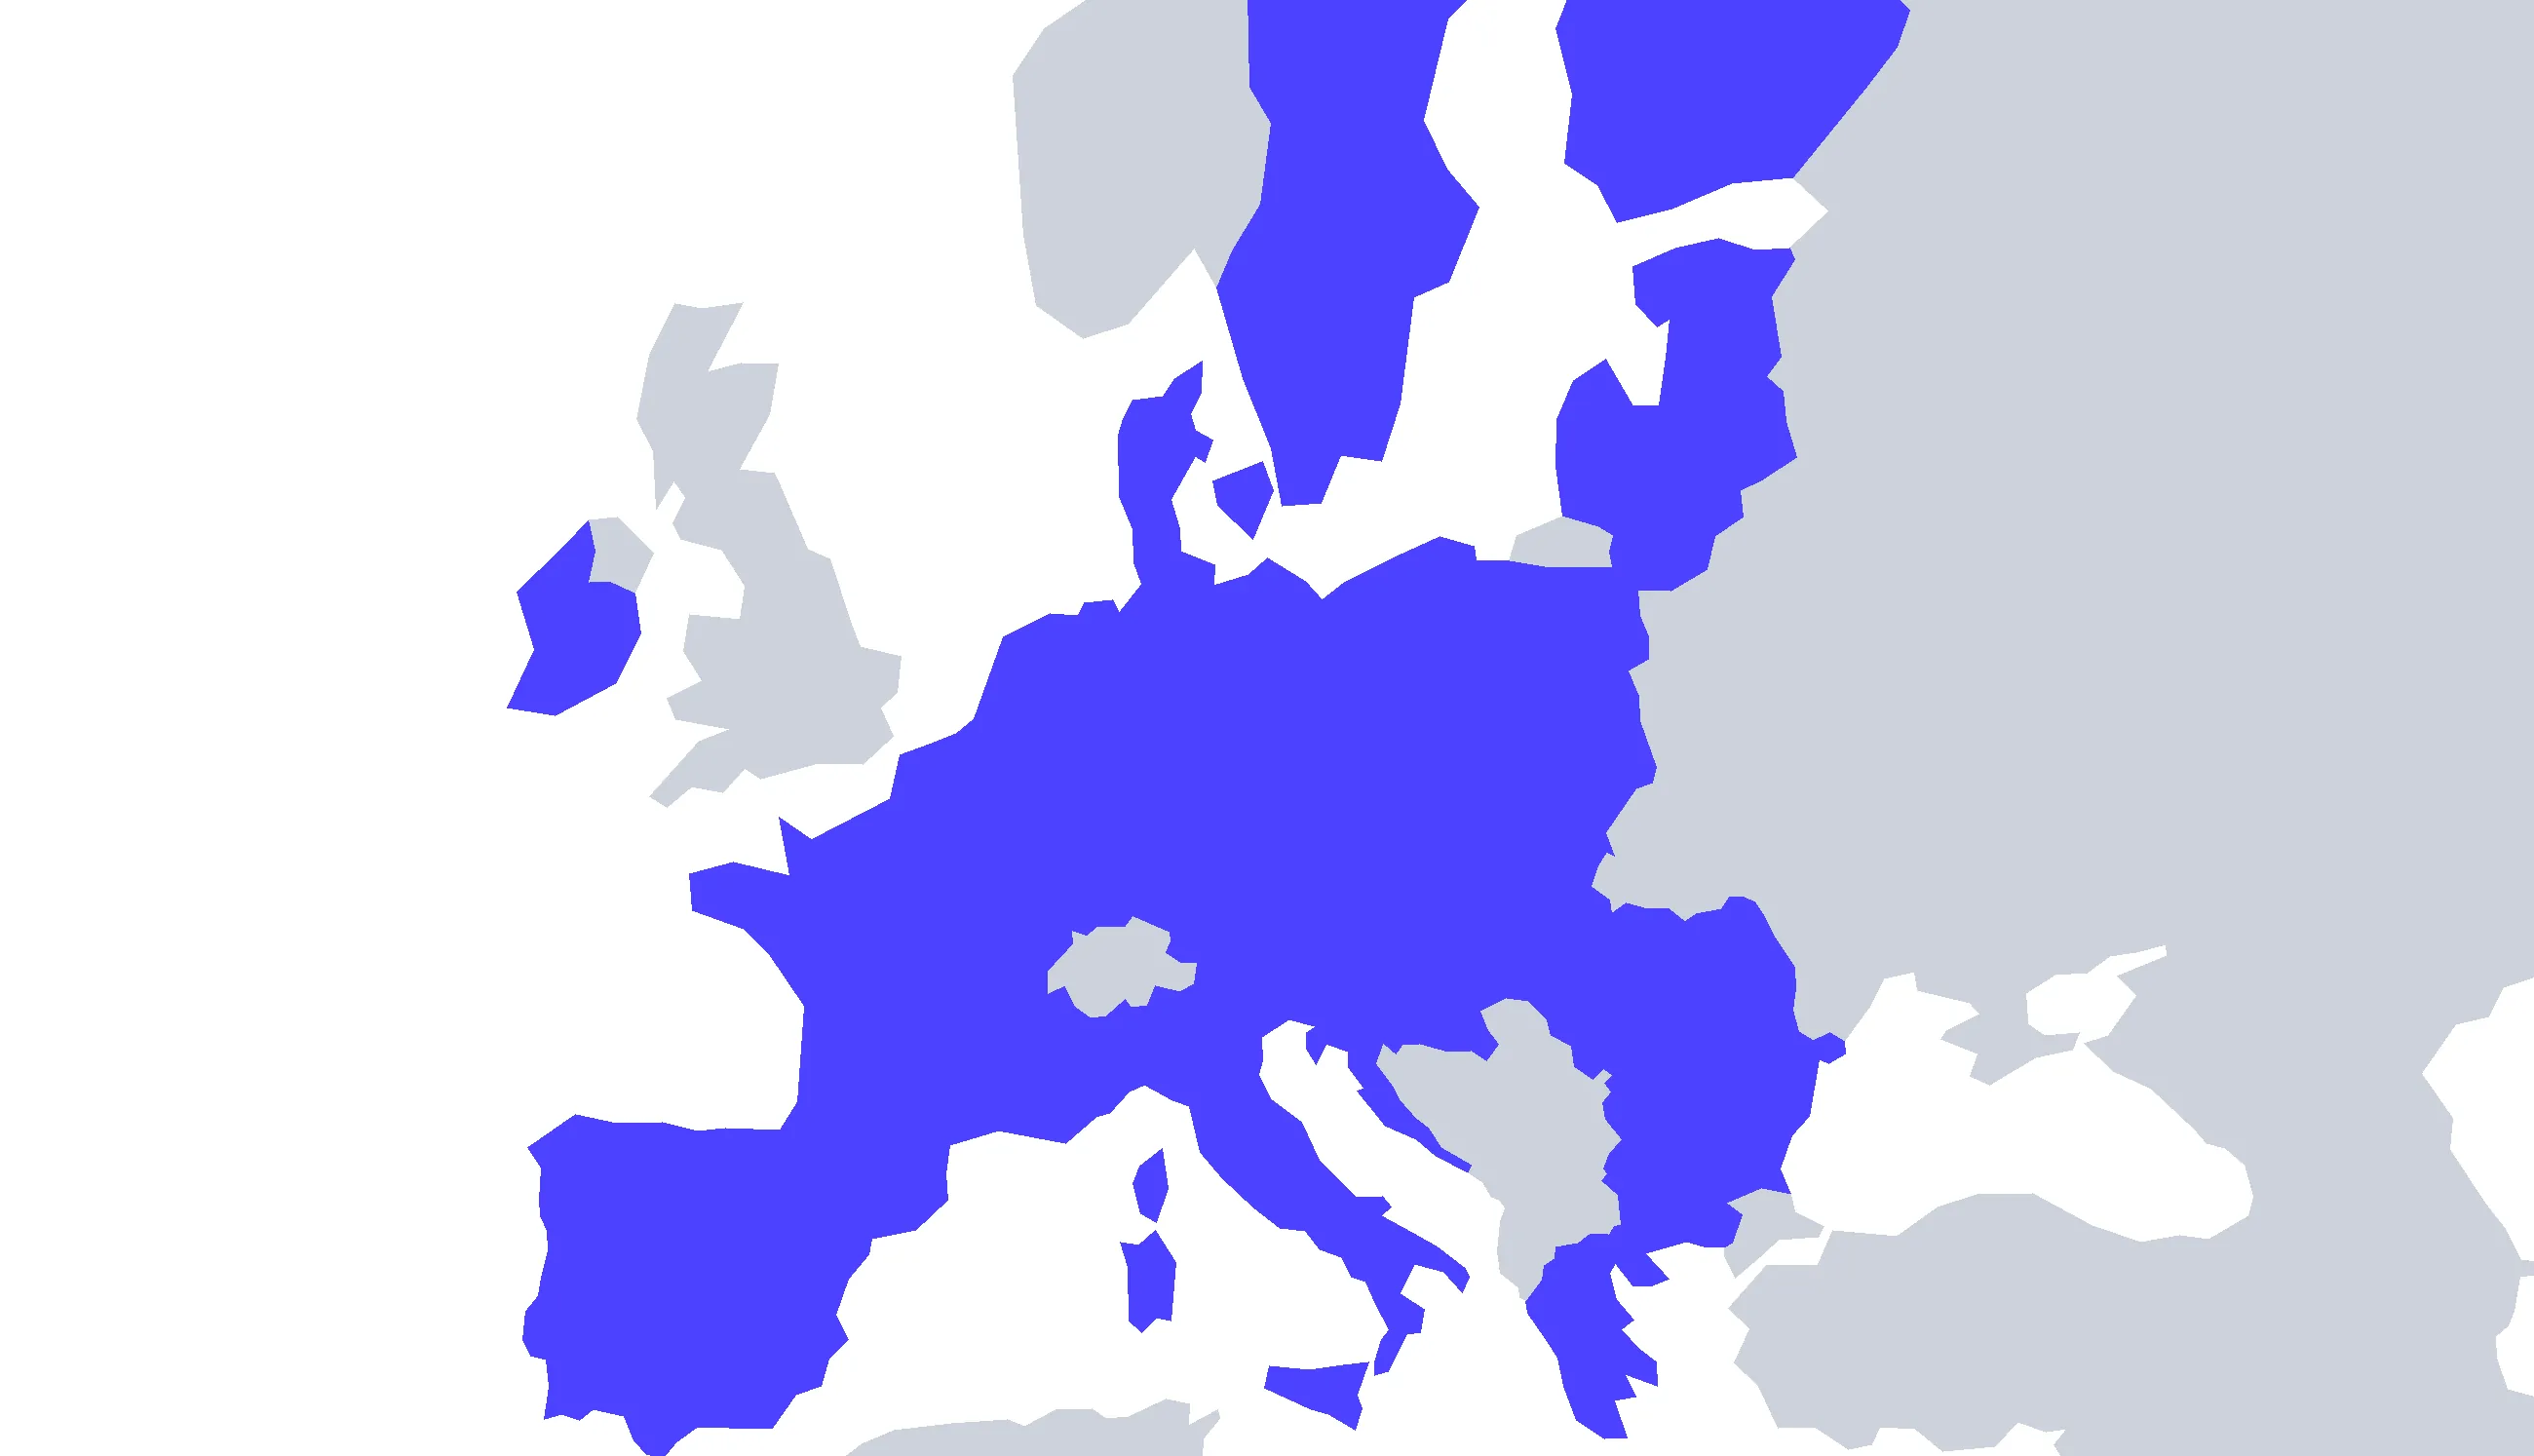
Map of Europe: customer data in Germany, model requests in Europe
Your chats and documents are stored encrypted in Germany.
Processing takes place in Europe, with Zero Data Retention.
Your output comes back in the quality you need, in the same interface.
The model provider does not store your request. Your data does not train any AI model; this is contractually excluded.
AI processing takes place exclusively in the EU. The DPA (data processing agreement) under Art. 28 GDPR is automatically part of the contract, and all data protection documents are available for download.
Your chats and documents are stored encrypted in Germany. The model provider does not store the request, and it is not used for any training.
Hosted in ISO 27001-certified German data centers; the cloud infrastructure is attested under BSI C5. External penetration tests included.
For professionals bound by secrecy, we conclude the agreement under § 203 StGB. We guarantee confidentiality contractually for every industry, not just technically.
Yes, that lies with you as the controller. Logicc's DPA, TOMs and security information feed into it as information about the service provider.
That depends on your legal basis under Art. 9 GDPR, and not every model is contractually approved for health data. Logicc provides the DPA, security information, the professional secrecy agreement and the TOMs.
Uploaded audio files are transcribed and, like all files, stored encrypted in Germany. You can delete them at any time, and a retention period can be set for the entire organisation.
Yes, from the Secure+ plan, and it can be concluded digitally in the app.
 Law firms & legal professionalsWhy § 203 StGB is not a ban on AI and how Logicc protects client confidentiality. →
 Public sectorWhat applies to social data and why Logicc is the European sovereign option. →
 Financial servicesWhat DORA requires and how Logicc supports you in meeting the requirements. →
Try it free for 7 days. No credit card required. Or book a demo
 DPA (data processing agreement)

 GPT 5.6 Terra
