The agreement under Art. 28 GDPR with annexes: processing details, subprocessors, TOMs.
Security and compliance
At Logicc, security is the foundation of the platform.
Storage in Germany, AI processing in the EU, DPA and professional secrecy agreement included. All evidence and contracts are available for download.
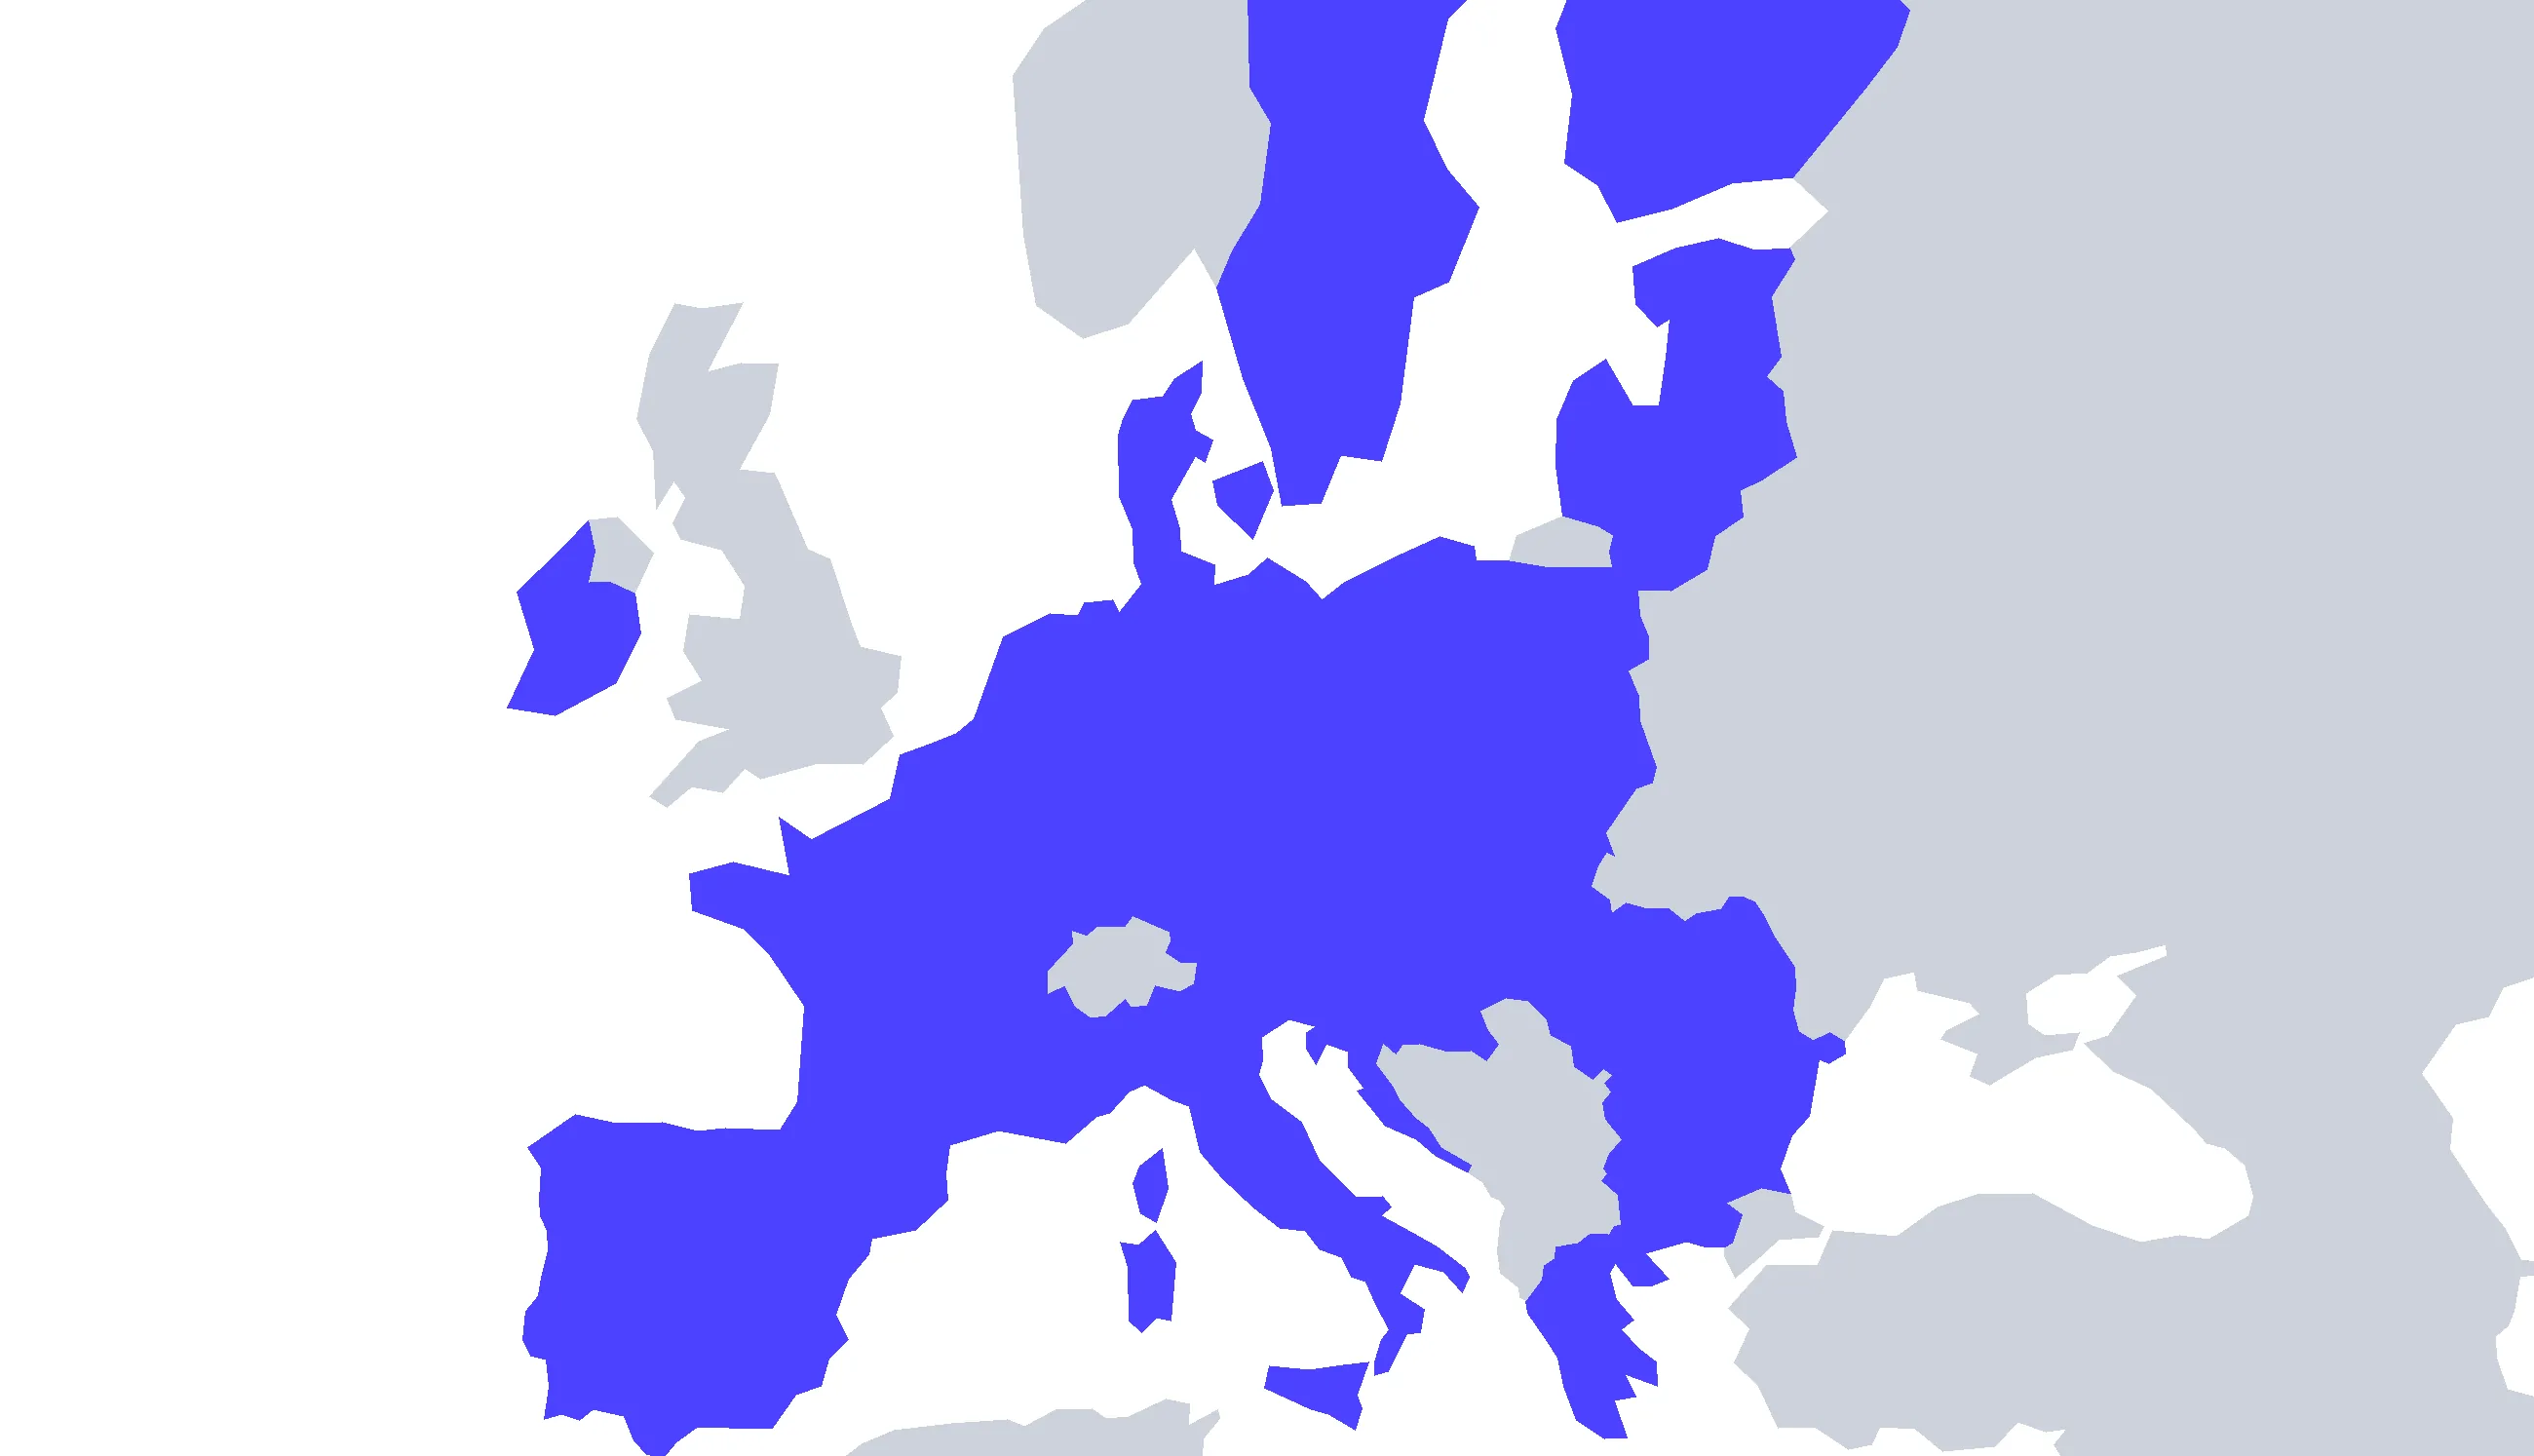
StorageGermany · encrypted
Model requestsEU region · Zero Data Retention
EU-27outside
Map of Europe: customer data in Germany, model requests in Europe
Evidence
Reviewed and documented.
GDPR: AI processing in the EU, DPA (data processing agreement) as a standard part of the contract.
BSI C5: The cloud infrastructure is attested against the BSI criteria catalogue (C5:2020 Type 2).
ISO 27001: All core data is stored in ISO 27001-certified data centres in Germany.
Professional secrecy: Agreement for law firms, medical practices and advisory firms, also for Austria and Switzerland.
The path of your data
The secure path of your data.
- Upload You enter data
Your chats and documents are stored encrypted in Germany.
encrypted - Request The request goes out
Processing takes place in Europe, with Zero Data Retention.
Region EU - Response You receive a response
Your output comes back in the quality you need, in the same interface.
Logicc interface - Afterwards Nothing stays with the provider
The model provider does not store your request. Your data does not train any AI model; this is contractually excluded.
Zero Data Retention
In detail
All the details for your data protection team.
Data storage
Where your data is stored and how it is protected.
Storage in Germany: Documents, chat histories and account data are stored exclusively in Germany, in ISO 27001-certified data centres operated by our partner Hetzner in Nürnberg and Falkenstein. Deliberately no US host.
Encryption: AES-256 at rest, TLS 1.3 in transit. Tenant separation via row-level security at database and application level.
Retention: You decide how long chats are stored: 30, 90 or 180 days, 1 or 2 years or unlimited, separately for general and project chats. After that, they are permanently deleted.
Deletion: You can delete individual documents and entire chat histories yourself at any time, irreversibly. When the contract ends, all data is deleted unless statutory retention obligations apply.
Processing
What happens with every request to a model.
Processing in Europe: OpenAI models run on Microsoft Azure in Sweden, Claude and Gemini on Google Cloud in Germany and Belgium.
Zero Data Retention: Contractually agreed with all model providers: the request is answered and not stored by the model provider, as far as technically possible.
No training: Your data doesn't train any AI model, ruled out both contractually and technically.
Model control: Admins decide which providers and which models are enabled in the organisation.
Access and accounts
Who can sign in and what they can see.
Two-factor and passkeys: Second factor via authenticator app or SMS, plus backup codes and passwordless sign-in with passkeys. Can be made mandatory for the entire organisation.
Single Sign-On: Sign-in via Microsoft Entra ID, Google Workspace, Okta and SAML 2.0, plus SCIM provisioning. From the Max plan.
Roles and groups: Permission management (RBAC) on all plans: admins, group admins and members, sharing by person, group or organisation.
Operation
How we protect the platform and have it tested.
Monitoring: 24/7 monitoring, web application firewall and DDoS protection.
Penetration tests: Regular tests by external security experts.
Subprocessors: The complete list is part of the DPA. We announce new subprocessors at least 15 days in advance, with a right to object.
Data protection officer: Externally appointed: Georg Schütz, KaMUX GmbH & Co. KG, registered with the Hamburg Commissioner for Data Protection and Freedom of Information.
Evidence
Verified by third parties, not just promised.
BSI C5: The cloud infrastructure of our hosting partner is attested under C5:2020 Type 2.
ISO 27001: The data centres where all core data is stored are ISO 27001 certified.
Certificates and audits: Access to certificates and audit reports from the Secure+ plan.
Professional secrecy
For lawyers, doctors, tax advisors and notaries.
Germany, Austria, Switzerland: Agreements under § 203 StGB, § 121 StGB (Austria) and Art. 321 StGB (Switzerland), signable digitally in the app, countersigned by Logicc. From the Secure+ plan.
Good to know: Some model providers are not covered by the agreement. Once it is concluded, their models are not available, but most models remain usable.
Measures
Our technical and organisational measures at a glance.
The binding TOMs are an annex to the data processing agreement.
Infrastructure
- C5-attested server infrastructure
- Data centres in Germany
- Network and backup concept
Data
- Encrypted storage
- Storage exclusively in Germany
- Data separation per organisation
AI-specific
- Zero Data Retention for every model request
- No training on customer data
- Model choice per task
Access
- Roles and permissions
- Authentication procedures
- Logging
Organisation
- Information security management according to ISO 27001
- DPA and TOMs as part of the contract
- Data protection officer
Operations and emergencies
- Incident process
- Recovery concept
- Status page
Subprocessors
Our subprocessors with their task and place of processing.
The binding list is in the annex to the DPA. We announce new subprocessors at least 15 days in advance, with a right to object.
Service providerPurposeLocation
Hosting and storageOperation of the platform, storage of persistent dataDE
Provider of the GPT modelsOperation of AI models via EU accessEU
Provider of the Claude modelsOperation of AI models via EU accessEU
Provider of the Gemini modelsOperation of AI models via EU accessEU
Mistral AIOperation of AI modelsEU
§ 203 StGB
The agreement under § 203 StGB for professionals bound by secrecy.
Agreement under § 203 StGB
Logicc provides law firms, medical practices and advisory firms with an agreement under § 203 StGB, together with the DPA and TOMs.
§ 203 in plain languageObligations of service providers
Logicc binds all relevant service providers, including the model providers, to confidentiality backed by criminal law.
Own employees
All Logicc employees are bound to confidentiality backed by criminal law.
Documents
Everything for approval.
How Logicc protects data technically and organisationally (Annex 3 of the DPA).
For professionals bound by secrecy such as law firms, medical practices and advisory firms.
How Logicc processes personal data on the website and platform.
The General Terms and Conditions of Logicc GmbH for the use of the platform and services.
C5 attestation excerpt from the hosting provider and completed security questionnaires.
For your industry
Every industry has its own rules.
Security by industry
 Law firms & legal professionalsWhy § 203 StGB is not a ban on AI and how Logicc protects client confidentiality. →
 Medicine & healthcareProcess patient data securely and in compliance with the law: what Art. 9 GDPR requires and how Logicc protects health data. →
 Public sectorWhat applies to social data and why Logicc is the European sovereign option. →
 Financial servicesWhat DORA requires and how Logicc supports you in meeting the requirements. →
FAQ
Frequently asked questions about security.
With concrete measures: storage in Germany, AI processing in the EU, a DPA (data processing agreement) under Art. 28 GDPR as part of the contract, a documented deletion concept and an external data protection officer.
AI processing takes place exclusively in the EU, with Zero Data Retention at the model provider. Training on your data is excluded by contract. We store chats and files encrypted in Germany.
Yes, from the Secure+ plan. You sign it digitally in the app, and corresponding agreements are available for Austria and Switzerland.
In normal operation, no one: employees and service providers have no access to the content. Support access only takes place on your documented instruction, limited to what is necessary in terms of time and personnel. All employees and relevant service providers are bound to confidentiality under penalty of law.
Yes. Individual documents and chats yourself at any time, automatically for the entire organisation via a retention period, and completely when the contract ends.
Yes. Send it to us via the contact form. Much of it can be answered in advance with this page and the DPA.

All documents in one place.
All documents for download, all answers in the demo. Or book a demo