What does DORA require?
The Digital Operational Resilience Act has applied since January 2025. Financial entities must manage their ICT risks and document, assess and monitor their ICT service providers.
 Larger organisation? Onboarding, training and a dedicated contact person.
What DORA requires and how Logicc supports you in meeting the requirements.
The Digital Operational Resilience Act has applied since January 2025. Financial entities must manage their ICT risks and document, assess and monitor their ICT service providers.
Documented security measures, an infrastructure attested under BSI C5 and all the information you need about us as an ICT service provider: DPA, TOMs, subprocessors, storage and processing locations.
AES-256 at rest, TLS 1.3 in transit, tenant separation via row-level security, 24/7 monitoring, a web application firewall and regular external penetration tests.
Logicc is a tool for texts and analyses, not a system for automated creditworthiness assessment or scoring. Under the EU AI Act, such applications are considered high-risk. Decisions remain with you.
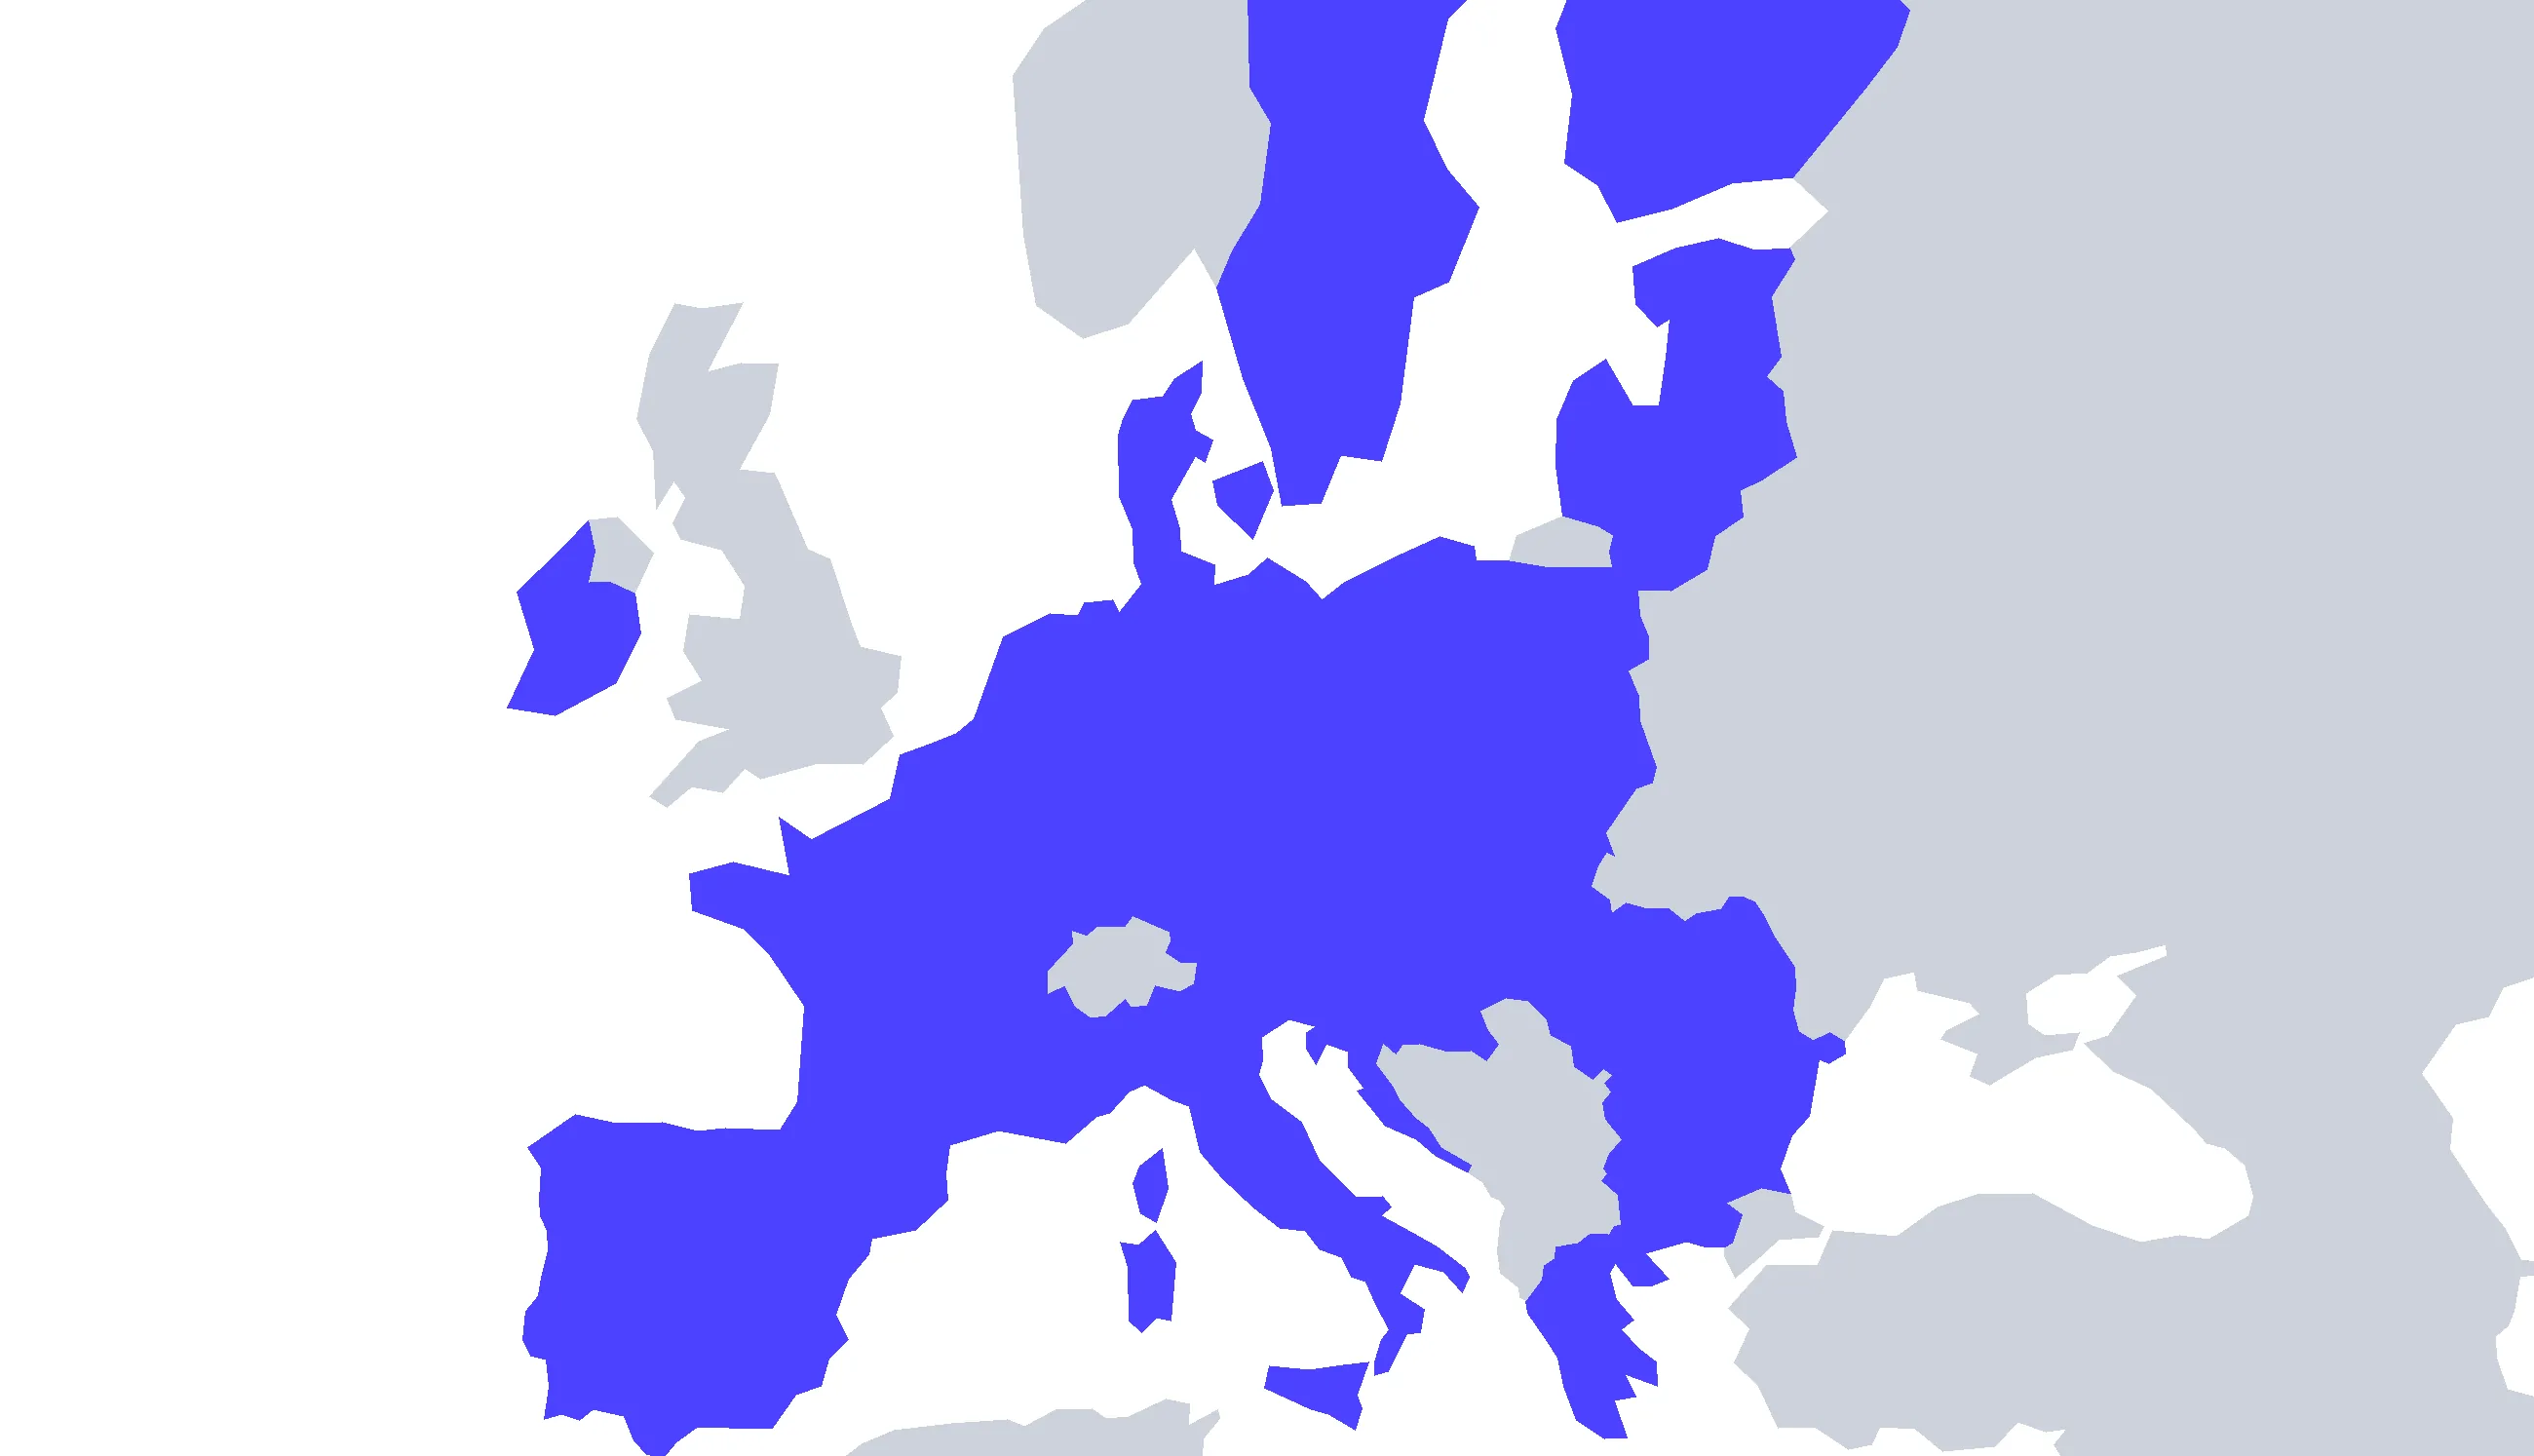
Map of Europe: customer data in Germany, model requests in Europe
Your chats and documents are stored encrypted in Germany.
Processing takes place in Europe, with Zero Data Retention.
Your output comes back in the quality you need, in the same interface.
The model provider does not store your request. Your data does not train any AI model; this is contractually excluded.
AI processing takes place exclusively in the EU. The DPA (data processing agreement) under Art. 28 GDPR is automatically part of the contract, and all data protection documents are available for download.
Your chats and documents are stored encrypted in Germany. The model provider does not store the request, and it is not used for any training.
Hosted in ISO 27001-certified German data centers; the cloud infrastructure is attested under BSI C5. External penetration tests included.
For professionals bound by secrecy, we conclude the agreement under § 203 StGB. We guarantee confidentiality contractually for every industry, not just technically.
Yes, with documented security measures and all the information your assessment and your register of information require.
Exclusively in Germany, encrypted. AI processing runs in the EU, with Zero Data Retention at the model provider.
Yes, from the Max plan: Microsoft Entra ID, Google Workspace, Okta and SAML 2.0, plus SCIM provisioning.
Hosting on dedicated servers is available on the Enterprise plan. Get in touch with us for details.
 Law firms & legal professionalsWhy § 203 StGB is not a ban on AI and how Logicc protects client confidentiality. →
 Medicine & healthcareProcess patient data securely and in compliance with the law: what Art. 9 GDPR requires and how Logicc protects health data. →
 Public sectorWhat applies to social data and why Logicc is the European sovereign option. →
Try it free for 7 days. No credit card required. Or book a demo
 DPA (data processing agreement) with list of subprocessors

 GPT 5.6 Terra
